Control Channel SSL/Data channel negotiation module. More...
#include "basic.h"#include "common.h"#include "crypto.h"#include "packet_id.h"#include "session_id.h"#include "reliable.h"#include "socket.h"#include "mtu.h"#include "options.h"#include "plugin.h"#include "ssl_common.h"#include "ssl_backend.h"#include "ssl_pkt.h"#include "tls_crypt.h"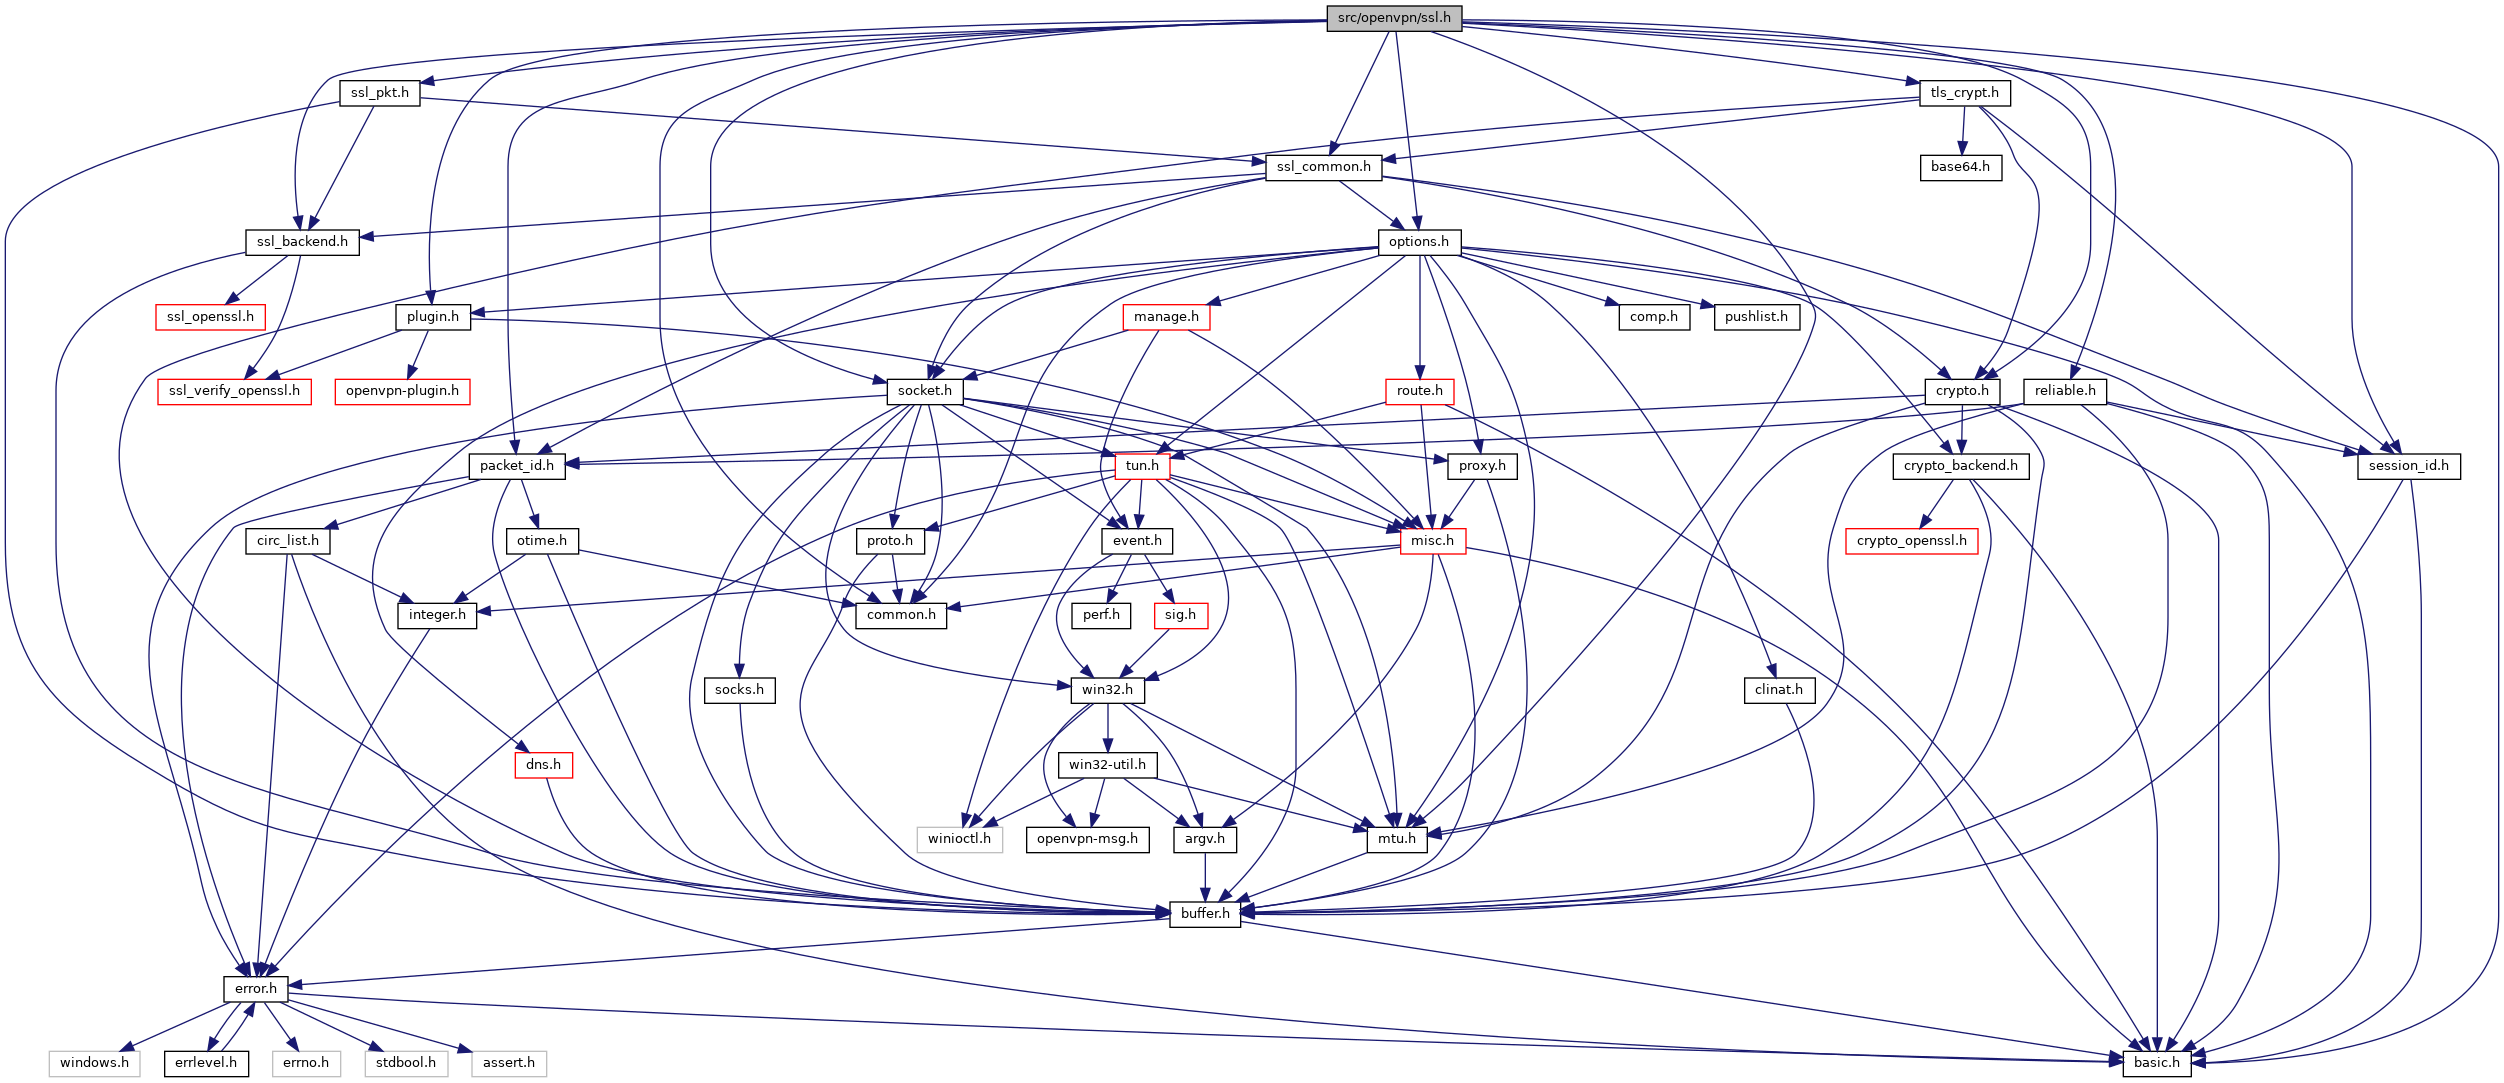
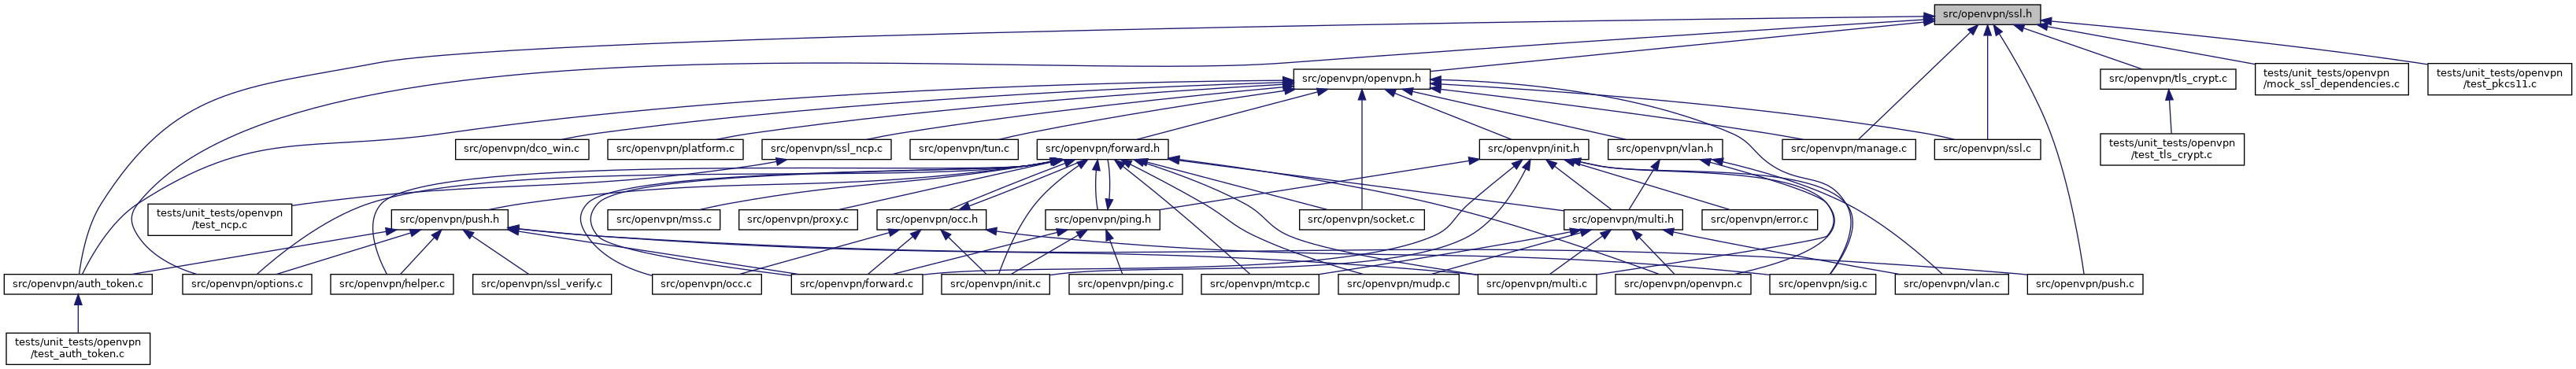
Go to the source code of this file.
Macros | |
| #define | KEY_EXPANSION_ID "OpenVPN" |
| #define | CONTROL_SEND_ACK_MAX 4 |
| #define | TLS_MULTI_REFRESH 15 /* call tls_multi_process once every n seconds */ |
| #define | TLS_MULTI_HORIZON |
| #define | TLS_OPTIONS_LEN 512 |
| #define | IV_PROTO_DATA_V2 (1 << 1) |
| Support P_DATA_V2. | |
| #define | IV_PROTO_REQUEST_PUSH (1 << 2) |
| Assume client will send a push request and server does not need to wait for a push-request to send a push-reply. | |
| #define | IV_PROTO_TLS_KEY_EXPORT (1 << 3) |
| Supports key derivation via TLS key material exporter [RFC5705]. | |
| #define | IV_PROTO_AUTH_PENDING_KW (1 << 4) |
| Supports signaling keywords with AUTH_PENDING, e.g. | |
| #define | IV_PROTO_NCP_P2P (1 << 5) |
| Support doing NCP in P2P mode. | |
| #define | IV_PROTO_DNS_OPTION (1 << 6) |
| Supports the –dns option introduced in version 2.6. | |
| #define | IV_PROTO_CC_EXIT_NOTIFY (1 << 7) |
| Support for explicit exit notify via control channel This also includes support for the protocol-flags pushed option. | |
| #define | IV_PROTO_AUTH_FAIL_TEMP (1 << 8) |
| Support for AUTH_FAIL,TEMP messages. | |
| #define | IV_PROTO_DYN_TLS_CRYPT (1 << 9) |
| Support to dynamic tls-crypt (renegotiation with TLS-EKM derived tls-crypt key) | |
| #define | IV_PROTO_DATA_EPOCH (1 << 10) |
| Support the extended packet id and epoch format for data channel packets. | |
| #define | IV_PROTO_DNS_OPTION_V2 (1 << 11) |
| Supports the –dns option after all the incompatible changes. | |
| #define | IV_PROTO_PUSH_UPDATE (1 << 12) |
| Supports push-update. | |
| #define | X509_USERNAME_FIELD_DEFAULT "CN" |
| #define | KEY_METHOD_2 2 |
| #define | KEY_METHOD_MASK 0x0F |
| #define | TLSMP_INACTIVE 0 |
| #define | TLSMP_ACTIVE 1 |
| #define | TLSMP_KILL 2 |
| #define | TLSMP_RECONNECT 3 |
| #define | TLSMP_RESTART 4 |
| the session cannot recover on its own and has to be restarted | |
| #define | PD_TLS_AUTH_HMAC_SIZE_MASK 0xFF |
| #define | PD_SHOW_DATA (1 << 8) |
| #define | PD_TLS (1 << 9) |
| #define | PD_VERBOSE (1 << 10) |
| #define | PD_TLS_CRYPT (1 << 11) |
Functions | |
| void | init_ssl_lib (void) |
| void | free_ssl_lib (void) |
| struct tls_root_ctx * | init_ssl (const struct options *options, bool in_chroot) |
| Build master SSL context object that serves for the whole of OpenVPN instantiation. | |
| int | tls_multi_process (struct tls_multi *multi, struct buffer *to_link, struct link_socket_actual **to_link_addr, struct link_socket_info *to_link_socket_info, interval_t *wakeup) |
| bool | tls_pre_decrypt (struct tls_multi *multi, const struct link_socket_actual *from, struct buffer *buf, struct crypto_options **opt, bool floated, const uint8_t **ad_start) |
| Determine whether an incoming packet is a data channel or control channel packet, and process accordingly. | |
| void | pem_password_setup (const char *auth_file) |
| void | enable_auth_user_pass (void) |
| void | auth_user_pass_setup (const char *auth_file, bool is_inline, bool username_only, const struct static_challenge_info *sc_info) |
| void | ssl_set_auth_nocache (void) |
| bool | ssl_get_auth_nocache (void) |
| void | ssl_purge_auth (const bool auth_user_pass_only) |
| void | ssl_set_auth_token (const char *token) |
| void | ssl_set_auth_token_user (const char *username) |
| bool | ssl_clean_auth_token (void) |
| void | ssl_purge_auth_challenge (void) |
| void | ssl_put_auth_challenge (const char *cr_str) |
| bool | tls_send_payload (struct key_state *ks, const uint8_t *data, size_t size) |
| bool | tls_rec_payload (struct tls_multi *multi, struct buffer *buf) |
| void | tls_update_remote_addr (struct tls_multi *multi, const struct link_socket_actual *addr) |
| Updates remote address in TLS sessions. | |
| bool | tls_session_update_crypto_params (struct tls_multi *multi, struct tls_session *session, struct options *options, struct frame *frame, struct frame *frame_fragment, struct link_socket_info *lsi, dco_context_t *dco) |
| Update TLS session crypto parameters (cipher and auth) and derive data channel keys based on the supplied options. | |
| static void | tls_wrap_free (struct tls_wrap_ctx *tls_wrap) |
| Free the elements of a tls_wrap_ctx structure. | |
| static bool | tls_initial_packet_received (const struct tls_multi *multi) |
| static int | tls_test_payload_len (const struct tls_multi *multi) |
| static void | tls_set_single_session (struct tls_multi *multi) |
| const char * | protocol_dump (struct buffer *buffer, unsigned int flags, struct gc_arena *gc) |
| bool | is_hard_reset_method2 (int op) |
| Given a key_method, return true if opcode represents the one of the hard_reset op codes for key-method 2. | |
| void | show_available_tls_ciphers (const char *cipher_list, const char *cipher_list_tls13, const char *tls_cert_profile) |
| void | tls_session_soft_reset (struct tls_multi *multi) |
| void | load_xkey_provider (void) |
| Load ovpn.xkey provider used for external key signing. | |
| bool | session_skip_to_pre_start (struct tls_session *session, struct tls_pre_decrypt_state *state, struct link_socket_actual *from) |
Functions for initialization and cleanup of tls_multi structures | |
| struct tls_multi * | tls_multi_init (struct tls_options *tls_options) |
Allocate and initialize a tls_multi structure. | |
| void | tls_multi_init_finalize (struct tls_multi *multi, int tls_mtu) |
Finalize initialization of a tls_multi structure. | |
| struct tls_auth_standalone * | tls_auth_standalone_init (struct tls_options *tls_options, struct gc_arena *gc) |
| void | tls_auth_standalone_free (struct tls_auth_standalone *tas) |
| Frees a standalone tls-auth verification object. | |
| void | tls_init_control_channel_frame_parameters (struct frame *frame, int tls_mtu) |
| void | tls_multi_init_set_options (struct tls_multi *multi, const char *local, const char *remote) |
| void | tls_multi_free (struct tls_multi *multi, bool clear) |
Cleanup a tls_multi structure and free associated memory allocations. | |
Functions for managing security parameter state for data channel packets | |
| void | tls_pre_encrypt (struct tls_multi *multi, struct buffer *buf, struct crypto_options **opt) |
| Choose the appropriate security parameters with which to process an outgoing packet. | |
| struct key_state * | tls_select_encryption_key (struct tls_multi *multi) |
| Selects the primary encryption that should be used to encrypt data of an outgoing packet. | |
| void | tls_prepend_opcode_v1 (const struct tls_multi *multi, struct buffer *buf) |
| Prepend a one-byte OpenVPN data channel P_DATA_V1 opcode to the packet. | |
| void | tls_prepend_opcode_v2 (const struct tls_multi *multi, struct buffer *buf) |
| Prepend an OpenVPN data channel P_DATA_V2 header to the packet. | |
| void | tls_post_encrypt (struct tls_multi *multi, struct buffer *buf) |
| Perform some accounting for the key state used. | |
Detailed Description
Control Channel SSL/Data channel negotiation module.
Definition in file ssl.h.
Macro Definition Documentation
◆ CONTROL_SEND_ACK_MAX
◆ IV_PROTO_AUTH_FAIL_TEMP
| #define IV_PROTO_AUTH_FAIL_TEMP (1 << 8) |
◆ IV_PROTO_AUTH_PENDING_KW
| #define IV_PROTO_AUTH_PENDING_KW (1 << 4) |
◆ IV_PROTO_CC_EXIT_NOTIFY
| #define IV_PROTO_CC_EXIT_NOTIFY (1 << 7) |
◆ IV_PROTO_DATA_EPOCH
| #define IV_PROTO_DATA_EPOCH (1 << 10) |
◆ IV_PROTO_DATA_V2
◆ IV_PROTO_DNS_OPTION
| #define IV_PROTO_DNS_OPTION (1 << 6) |
◆ IV_PROTO_DNS_OPTION_V2
| #define IV_PROTO_DNS_OPTION_V2 (1 << 11) |
◆ IV_PROTO_DYN_TLS_CRYPT
| #define IV_PROTO_DYN_TLS_CRYPT (1 << 9) |
◆ IV_PROTO_NCP_P2P
| #define IV_PROTO_NCP_P2P (1 << 5) |
◆ IV_PROTO_PUSH_UPDATE
◆ IV_PROTO_REQUEST_PUSH
| #define IV_PROTO_REQUEST_PUSH (1 << 2) |
◆ IV_PROTO_TLS_KEY_EXPORT
| #define IV_PROTO_TLS_KEY_EXPORT (1 << 3) |
◆ KEY_EXPANSION_ID
◆ KEY_METHOD_2
◆ KEY_METHOD_MASK
◆ PD_SHOW_DATA
◆ PD_TLS
◆ PD_TLS_AUTH_HMAC_SIZE_MASK
◆ PD_TLS_CRYPT
◆ PD_VERBOSE
◆ TLS_MULTI_HORIZON
| #define TLS_MULTI_HORIZON |
◆ TLS_MULTI_REFRESH
| #define TLS_MULTI_REFRESH 15 /* call tls_multi_process once every n seconds */ |
◆ TLS_OPTIONS_LEN
◆ TLSMP_ACTIVE
◆ TLSMP_INACTIVE
◆ TLSMP_KILL
◆ TLSMP_RECONNECT
◆ TLSMP_RESTART
| #define TLSMP_RESTART 4 |
◆ X509_USERNAME_FIELD_DEFAULT
Function Documentation
◆ auth_user_pass_setup()
| void auth_user_pass_setup | ( | const char * | auth_file, |
| bool | is_inline, | ||
| bool | username_only, | ||
| const struct static_challenge_info * | sc_info | ||
| ) |
Definition at line 302 of file ssl.c.
References auth_challenge, auth_token, auth_user_pass, static_challenge_info::challenge_text, user_pass::defined, static_challenge_info::flags, get_user_pass(), get_user_pass_cr(), GET_USER_PASS_DYNAMIC_CHALLENGE, GET_USER_PASS_INLINE_CREDS, GET_USER_PASS_MANAGEMENT, GET_USER_PASS_STATIC_CHALLENGE, GET_USER_PASS_STATIC_CHALLENGE_CONCAT, GET_USER_PASS_STATIC_CHALLENGE_ECHO, GET_USER_PASS_USERNAME_ONLY, SC_CONCAT, SC_ECHO, unprotect_user_pass(), and UP_TYPE_AUTH.
Referenced by init_query_passwords(), and key_method_2_write().
◆ enable_auth_user_pass()
| void enable_auth_user_pass | ( | void | ) |
Definition at line 296 of file ssl.c.
References auth_user_pass_enabled.
Referenced by init_query_passwords().
◆ free_ssl_lib()
| void free_ssl_lib | ( | void | ) |
Definition at line 242 of file ssl.c.
References crypto_uninit_lib(), and tls_free_lib().
Referenced by uninit_static().
◆ init_ssl()
| struct tls_root_ctx * init_ssl | ( | const struct options * | options, |
| bool | in_chroot | ||
| ) |
Build master SSL context object that serves for the whole of OpenVPN instantiation.
Definition at line 525 of file ssl.c.
References ALLOC_OBJ_CLEAR, BSTR, options::ca_file, options::ca_file_inline, options::ca_path, options::cert_file, options::cert_file_inline, options::chroot_dir, options::cipher_list, options::cipher_list_tls13, options::crl_file, options::crl_file_inline, options::cryptoapi_cert, options::dh_file, options::dh_file_inline, options::ecdh_curve, options::extra_certs_file, options::extra_certs_file_inline, gc, gc_free(), gc_new(), key_is_external(), buffer::len, load_xkey_provider(), M_WARN, options::management_certificate, options::management_flags, management_query_cert(), MF_EXTERNAL_CERT, MF_EXTERNAL_KEY, msg, options::pkcs12_file, options::pkcs12_file_inline, prepend_dir(), options::priv_key_file, options::priv_key_file_inline, options::ssl_flags, SSLF_CRL_VERIFY_DIR, options::tls_cert_profile, tls_clear_error(), tls_ctx_check_cert_time(), tls_ctx_free(), tls_ctx_load_ca(), tls_ctx_load_cert_file(), tls_ctx_load_cryptoapi(), tls_ctx_load_dh_params(), tls_ctx_load_ecdh_params(), tls_ctx_load_extra_certs(), tls_ctx_load_pkcs12(), tls_ctx_load_priv_file(), tls_ctx_new(), tls_ctx_reload_crl(), tls_ctx_restrict_ciphers(), tls_ctx_restrict_ciphers_tls13(), tls_ctx_set_cert_profile(), tls_ctx_set_options(), tls_ctx_set_tls_groups(), tls_ctx_use_management_external_key(), options::tls_groups, and options::tls_server.
Referenced by do_init_crypto_tls_c1().
◆ init_ssl_lib()
| void init_ssl_lib | ( | void | ) |
Definition at line 234 of file ssl.c.
References crypto_init_lib(), and tls_init_lib().
Referenced by init_static().
◆ is_hard_reset_method2()
| bool is_hard_reset_method2 | ( | int | op | ) |
Given a key_method, return true if opcode represents the one of the hard_reset op codes for key-method 2.
Definition at line 788 of file ssl.c.
References P_CONTROL_HARD_RESET_CLIENT_V2, P_CONTROL_HARD_RESET_CLIENT_V3, and P_CONTROL_HARD_RESET_SERVER_V2.
Referenced by tls_pre_decrypt(), and tls_process_state().
◆ load_xkey_provider()
| void load_xkey_provider | ( | void | ) |
Load ovpn.xkey provider used for external key signing.
Load ovpn.xkey provider used for external key signing.
Setup ovpn.xey provider for signing with external keys. It is loaded into a custom library context so as not to pollute the default context. Alternatively we could override any system-wide property query set on the default context. But we want to avoid that.
Definition at line 2661 of file ssl_openssl.c.
References check_malloc_return(), M_NONFATAL, msg, and tls_libctx.
Referenced by init_ssl().
◆ pem_password_setup()
| void pem_password_setup | ( | const char * | auth_file | ) |
Definition at line 257 of file ssl.c.
References get_user_pass(), GET_USER_PASS_MANAGEMENT, GET_USER_PASS_PASSWORD_ONLY, passbuf, user_pass::password, unprotect_user_pass(), and UP_TYPE_PRIVATE_KEY.
Referenced by init_query_passwords(), and pem_password_callback().
◆ protocol_dump()
Definition at line 4327 of file ssl.c.
References alloc_buf_gc(), ASSERT, BLEN, BPTR, BSTR, buf_printf(), buf_read(), format_hex(), gc, buffer::len, MAX_HMAC_KEY_LENGTH, ntohpid, P_ACK_V1, P_DATA_V1, P_DATA_V2, P_KEY_ID_MASK, P_OPCODE_SHIFT, packet_id_format, packet_id_net_print(), packet_id_read(), packet_opcode_name(), PD_SHOW_DATA, PD_TLS, PD_TLS_AUTH_HMAC_SIZE_MASK, PD_TLS_CRYPT, PD_VERBOSE, reliable_ack_print(), session_id_print(), session_id_read(), and TLS_CRYPT_TAG_SIZE.
◆ session_skip_to_pre_start()
| bool session_skip_to_pre_start | ( | struct tls_session * | session, |
| struct tls_pre_decrypt_state * | state, | ||
| struct link_socket_actual * | from | ||
| ) |
Definition at line 2602 of file ssl.c.
References session::key, KS_PRIMARY, reliable::packet_id, key_state::rec_reliable, key_state::remote_addr, key_state::session_id_remote, session_move_pre_start(), and key_state::state.
Referenced by handle_connection_attempt().
◆ show_available_tls_ciphers()
| void show_available_tls_ciphers | ( | const char * | cipher_list, |
| const char * | cipher_list_tls13, | ||
| const char * | tls_cert_profile | ||
| ) |
Definition at line 4302 of file ssl.c.
References show_available_tls_ciphers_list(), TLS_VER_1_3, and tls_version_max().
Referenced by print_openssl_info().
◆ ssl_clean_auth_token()
| bool ssl_clean_auth_token | ( | void | ) |
Definition at line 384 of file ssl.c.
References auth_token, user_pass::defined, and purge_user_pass().
Referenced by man_forget_passwords(), man_reset_client_socket(), and receive_auth_failed().
◆ ssl_get_auth_nocache()
| bool ssl_get_auth_nocache | ( | void | ) |
Definition at line 360 of file ssl.c.
References user_pass::nocache, and passbuf.
Referenced by options_postprocess_mutate_ce().
◆ ssl_purge_auth()
| void ssl_purge_auth | ( | const bool | auth_user_pass_only | ) |
Definition at line 395 of file ssl.c.
References auth_user_pass, passbuf, purge_user_pass(), and ssl_purge_auth_challenge().
Referenced by do_init_crypto_tls_c1(), man_forget_passwords(), man_reset_client_socket(), receive_auth_failed(), and server_pushed_signal().
◆ ssl_purge_auth_challenge()
| void ssl_purge_auth_challenge | ( | void | ) |
Definition at line 413 of file ssl.c.
References auth_challenge.
Referenced by ssl_purge_auth(), and ssl_put_auth_challenge().
◆ ssl_put_auth_challenge()
| void ssl_put_auth_challenge | ( | const char * | cr_str | ) |
Definition at line 420 of file ssl.c.
References auth_challenge, ssl_purge_auth_challenge(), and string_alloc().
Referenced by receive_auth_failed().
◆ ssl_set_auth_nocache()
| void ssl_set_auth_nocache | ( | void | ) |
Definition at line 350 of file ssl.c.
References auth_user_pass, user_pass::nocache, and passbuf.
Referenced by add_option().
◆ ssl_set_auth_token()
| void ssl_set_auth_token | ( | const char * | token | ) |
Definition at line 369 of file ssl.c.
References auth_token, and set_auth_token().
Referenced by add_option().
◆ ssl_set_auth_token_user()
| void ssl_set_auth_token_user | ( | const char * | username | ) |
Definition at line 375 of file ssl.c.
References auth_token, set_auth_token_user(), and user_pass::username.
Referenced by add_option().
◆ tls_initial_packet_received()
|
inlinestatic |
Definition at line 492 of file ssl.h.
References tls_multi::n_sessions.
Referenced by check_server_poll_timeout(), and process_outgoing_link().
◆ tls_multi_process()
| int tls_multi_process | ( | struct tls_multi * | multi, |
| struct buffer * | to_link, | ||
| struct link_socket_actual ** | to_link_addr, | ||
| struct link_socket_info * | to_link_socket_info, | ||
| interval_t * | wakeup | ||
| ) |
Definition at line 3365 of file ssl.c.
References link_socket_addr::actual, key_state::authenticated, CAS_CONNECT_DONE, CAS_PENDING, CAS_RECONNECT_PENDING, CAS_WAITING_AUTH, D_TLS_DEBUG, D_TLS_DEBUG_LOW, D_TLS_ERRORS, dmsg, gc, gc_free(), gc_new(), get_key_scan(), get_primary_key(), tls_options::gremlin, session::key, tls_session::key, KEY_GEN_DCO_DESYNC, KEY_GEN_OK, KEY_SCAN_SIZE, key_state_ssl_shutdown(), KS_AUTH_FALSE, KS_AUTH_TRUE, KS_LAME_DUCK, KS_PRIMARY, key_state::ks_ssl, lame_duck_must_die(), link_socket_actual_defined(), link_socket_info::lsa, move_session(), msg, tls_multi::multi_state, tls_multi::n_hard_errors, tls_multi::n_soft_errors, tls_multi::opt, print_link_socket_actual(), key_state::remote_addr, resend_auth_token_renegotiation(), reset_session(), S_ACTIVE, S_ERROR, S_ERROR_PRE, S_GENERATED_KEYS, S_INITIAL, tls_multi::session, session_id_print(), key_state::session_id_remote, tls_options::single_session, key_state::state, state_name(), status, TLS_AUTHENTICATED, TLS_AUTHENTICATION_FAILED, tls_authentication_status(), TLS_AUTHENTICATION_SUCCEEDED, tls_clear_error(), tls_process(), tls_session_free(), tls_session_generate_data_channel_keys(), TLSMP_ACTIVE, TLSMP_INACTIVE, TLSMP_KILL, TLSMP_RECONNECT, TLSMP_RESTART, TM_ACTIVE, TM_INITIAL, TM_LAME_DUCK, TM_SIZE, tls_multi::to_link_addr, and update_time().
Referenced by check_tls().
◆ tls_rec_payload()
Definition at line 4249 of file ssl.c.
References ASSERT, BLEN, buf_copy(), get_key_scan(), buffer::len, key_state::plaintext_read_buf, S_ACTIVE, key_state::state, and tls_clear_error().
Referenced by check_incoming_control_channel().
◆ tls_send_payload()
| bool tls_send_payload | ( | struct key_state * | ks, |
| const uint8_t * | data, | ||
| size_t | size | ||
| ) |
Definition at line 4216 of file ssl.c.
References ASSERT, buffer_list_new(), buffer_list_push_data(), key_state_write_plaintext_const(), key_state::ks_ssl, key_state::paybuf, S_ACTIVE, key_state::state, and tls_clear_error().
Referenced by send_control_channel_string_dowork().
◆ tls_session_soft_reset()
| void tls_session_soft_reset | ( | struct tls_multi * | multi | ) |
Definition at line 1833 of file ssl.c.
References key_state_soft_reset(), tls_multi::session, and TM_ACTIVE.
Referenced by process_incoming_dco().
◆ tls_session_update_crypto_params()
| bool tls_session_update_crypto_params | ( | struct tls_multi * | multi, |
| struct tls_session * | session, | ||
| struct options * | options, | ||
| struct frame * | frame, | ||
| struct frame * | frame_fragment, | ||
| struct link_socket_info * | lsi, | ||
| dco_context_t * | dco | ||
| ) |
Update TLS session crypto parameters (cipher and auth) and derive data channel keys based on the supplied options.
Does nothing if keys are already generated.
- Parameters
-
multi The TLS object for this instance. session The TLS session to update. options The options to use when updating session. frame The frame options for this session (frame overhead is adjusted based on the selected cipher/auth). frame_fragment The fragment frame options. lsi link socket info to adjust MTU related options depending on the current protocol dco The dco context to perform dco_set_peer() whenever a crypto param update occurs.
- Returns
- true if updating succeeded or keys are already generated, false otherwise.
Definition at line 1705 of file ssl.c.
References check_session_cipher(), options::imported_protocol_flags, and tls_session_update_crypto_params_do_work().
Referenced by do_deferred_options_part2(), do_deferred_p2p_ncp(), and multi_client_generate_tls_keys().
◆ tls_set_single_session()
|
inlinestatic |
Definition at line 512 of file ssl.h.
References tls_multi::opt, and tls_options::single_session.
Referenced by schedule_exit().
◆ tls_test_payload_len()
|
inlinestatic |
Definition at line 498 of file ssl.h.
References BLEN, get_primary_key(), key_state::plaintext_read_buf, S_ACTIVE, and key_state::state.
Referenced by check_incoming_control_channel(), and pre_select().
◆ tls_update_remote_addr()
| void tls_update_remote_addr | ( | struct tls_multi * | multi, |
| const struct link_socket_actual * | addr | ||
| ) |
Updates remote address in TLS sessions.
- Parameters
-
multi - Tunnel to update addr - new address
Definition at line 4274 of file ssl.c.
References D_TLS_KEYSELECT, dmsg, gc, gc_free(), gc_new(), session::key, KS_SIZE, link_socket_actual_defined(), link_socket_actual_match(), print_link_socket_actual(), key_state::remote_addr, tls_multi::session, and TM_SIZE.
Referenced by multi_process_float().
◆ tls_wrap_free()
|
inlinestatic |
Free the elements of a tls_wrap_ctx structure.
Definition at line 474 of file ssl.h.
References tls_wrap_ctx::cleanup_key_ctx, free_buf(), free_key_ctx_bi(), crypto_options::key_ctx_bi, tls_wrap_ctx::opt, tls_wrap_ctx::original_wrap_keydata, crypto_options::packet_id, packet_id_free(), packet_id_initialized(), secure_memzero(), and tls_wrap_ctx::work.
Referenced by test_tls_crypt_secure_reneg_key(), tls_crypt_v2_unwrap_checks(), tls_crypt_v2_wrap_unwrap_invalid(), tls_crypt_v2_wrap_unwrap_max_metadata(), and tls_session_free().